1. Identify
Log risks in a central ISO 27001 risk register with ownership, sources, and status—so leadership is not chasing five conflicting spreadsheets.
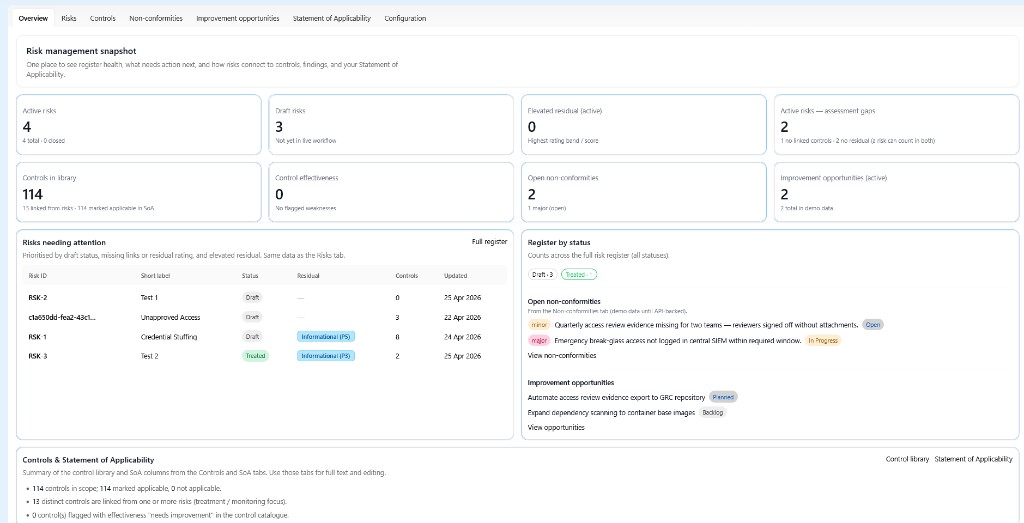
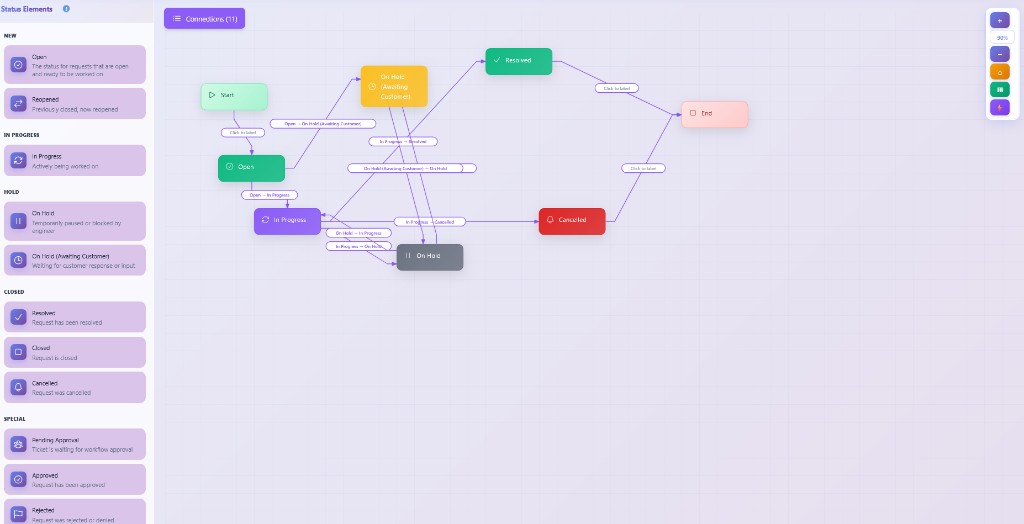
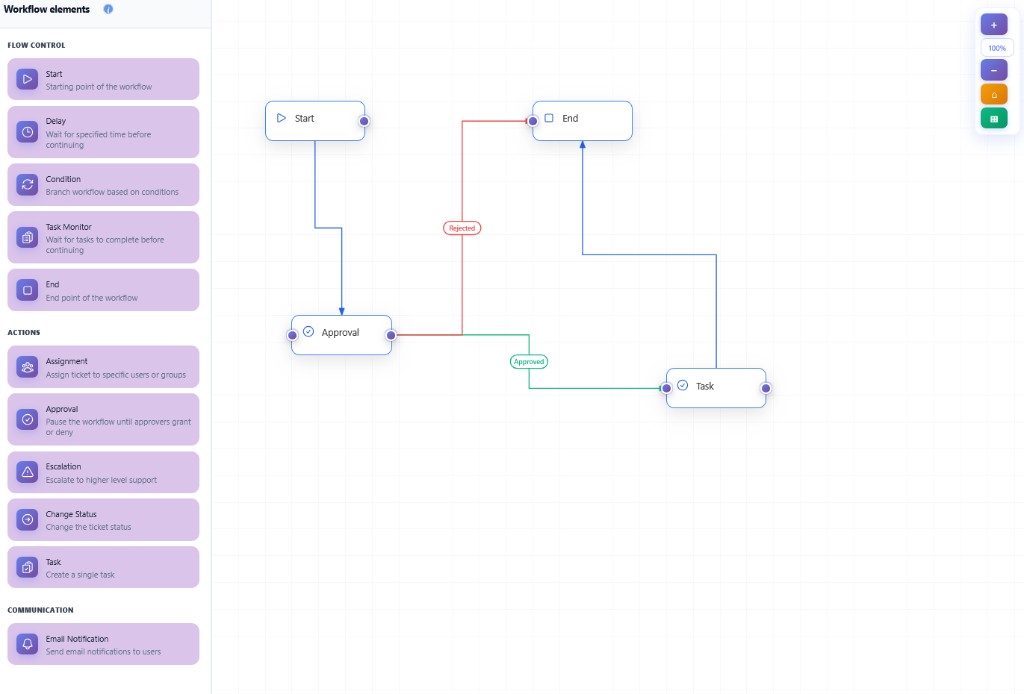
Leading GRC platforms emphasise a continuous risk lifecycle. ISMSVision covers the same auditor expectations—without hiding pricing behind a demo wall—and includes internal auditing in the same module.
Log risks in a central ISO 27001 risk register with ownership, sources, and status—so leadership is not chasing five conflicting spreadsheets.
Score likelihood and impact on a configurable risk matrix. Communicate priority with heat-map clarity instead of subjective “how red is red?” debates.
Record treatment plans (mitigate, transfer, avoid, or accept), map mitigating controls, and keep follow-up visible until residual risk is acceptable.
Keep reviews living—and run internal audits from the same Risk Management licence with schedules, checklists, and 384 ISO questions. Raise NCs, risks, and OFIs from findings.
Match the topics buyers search for when comparing risk management software for ISO 27001: register, assessment, treatment, control mapping, Statement of Applicability, and internal audit. Pair with Document Management for policy evidence and Supplier Management for third-party risk. See module pricing or Auditing for assurance detail.
A living register with owners, sources, and status—built for auditors who ask “show me the current risk list,” not last quarter’s export.
Describe scenarios and assess them consistently with structured fields—reducing gut-feel spreadsheet scoring.
Set likelihood and impact scales with a visual matrix so priority is clear to leadership and assessors.
Track mitigate / transfer / avoid / accept decisions and follow-up actions so risks do not stall in “we are monitoring” limbo.
Connect risks to the controls that mitigate them—so treatment plans map to what you actually operate and test.
Keep SoA applicability and justification notes with the same control library used for risk treatment—one story for assessors.
Unlike tools that sell audit as a separate add-on, ISMSVision includes audit schedule, calendar, checklists, and a 384-question ISO 27001/27002 bank in Risk Management.
Public list pricing from £30/user/month—compare openly instead of waiting on enterprise quote cycles.
Risks, controls, SoA, suppliers, and documents reference each other—not siloed exports.
Clear records, treatment history, and included internal audit workflows when assessors ask “show me”.
From £30 per user per month (GBP)—no sales-gated quote for core risk & audit; see full pricing.
Start a free trial and evaluate the risk register yourself.
Start a trial, compare public module pricing, or talk to sales about a phased ISMS rollout.
Start free trial View module pricingISO 27001 requires you to identify information security risks, analyse likelihood and impact, decide treatment, and keep documented evidence. Auditors typically review the risk register, treatment decisions, and how risks map to controls and the Statement of Applicability.
Yes. Maintain a living risk register with owners and status, link risks to controls, and produce Statement of Applicability (SoA) justification notes from the same control library.
Record treatment decisions such as mitigate, transfer, avoid, or accept, with ownership and follow-up so risks do not stall as unreviewed spreadsheet rows.
Map risks to your control library for treatment evidence. Internal auditing is included in the same module—schedule, checklists, and a 384-question ISO 27001/27002 bank—so findings can raise non-conformities, risks, or opportunities for improvement.
Yes. Configure likelihood and impact scales and the visual risk matrix to match your organisation’s risk appetite and assessment methodology.
Risk Management is publicly priced from £30 per user per month, with free trials and modular licensing. Auditing is included—no separate audit licence—so you are not forced into a sales-gated quote for core ISO 27001 risk and assurance workflows.